33 points petecooper 46 minutes ago 13 comments
umbula 42 minutes ago | parent
mjac 40 minutes ago | parent
umbula 37 minutes ago | parent
Joel_Mckay 12 minutes ago | parent
Checking the deb package release notes, will disclose which CVE are fixed.
Looking at just the 8.5-fpm or Apache mod_php will not indicate the system is still not patched. They both should be fixed as of last week if auto-updates have run.
If more CVE/RCE have dropped (we should expect the next year will have many), than it may take weeks for the patch to propagate across the ecosystem. =3
esskay 25 minutes ago | parent
nubinetwork 19 minutes ago | parent
petecooper 35 minutes ago | parent
  https://github.com/php/php-src/releases/tag/php-8.2.36
  https://github.com/php/php-src/releases/tag/php-8.3.37
  https://github.com/php/php-src/releases/tag/php-8.4.28
  https://github.com/php/php-src/releases/tag/php-8.5.13
  https://github.com/php/php-src/releases/tag/php-8.6.0
mjac 33 minutes ago | parent
showerst 28 minutes ago | parent
https://github.com/php/php-src/security/advisories/GHSA-8mjj...
Requires the following php.ini settings -- fatal_error_backtraces=1 and zend.exception_ignore_args=0
zend.exception_ignore_args is 1 by default.
https://github.com/php/php-src/security/advisories/GHSA-gr4f...
Doesn't have a setting mitigation but doesn't seem trivial to set up.
https://github.com/php/php-src/security/advisories/GHSA-gr4f...
Doesn't have a setting mitigation but doesn't seem trivial to set up.
https://github.com/php/php-src/security/advisories/GHSA-658j...
Requires session.upload_progress.enabled=1 which many people disabled as a mitigation to the earlier CVEs. If you haven't, you should disable it if possible.
This batch requires an immediate patch in case someone gets reliable exploit for those RCEs, but it doesn't appear to be 'take down the websites' level of bad.
tyilo 16 minutes ago | parent
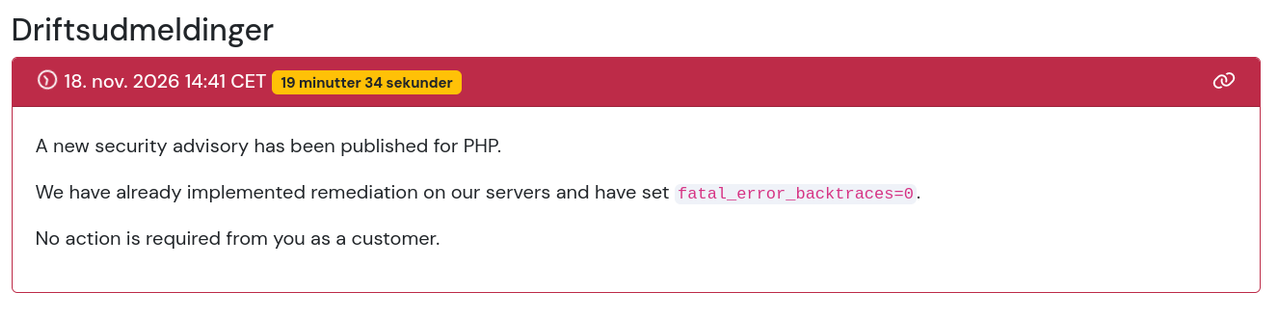
Screenshot taken at around 2026-11-18 14:00 UTC.
They seem to have accidentally posted that instead of the fix to nginx.